Assurance and compliance
Autonomous, yet every step auditable.
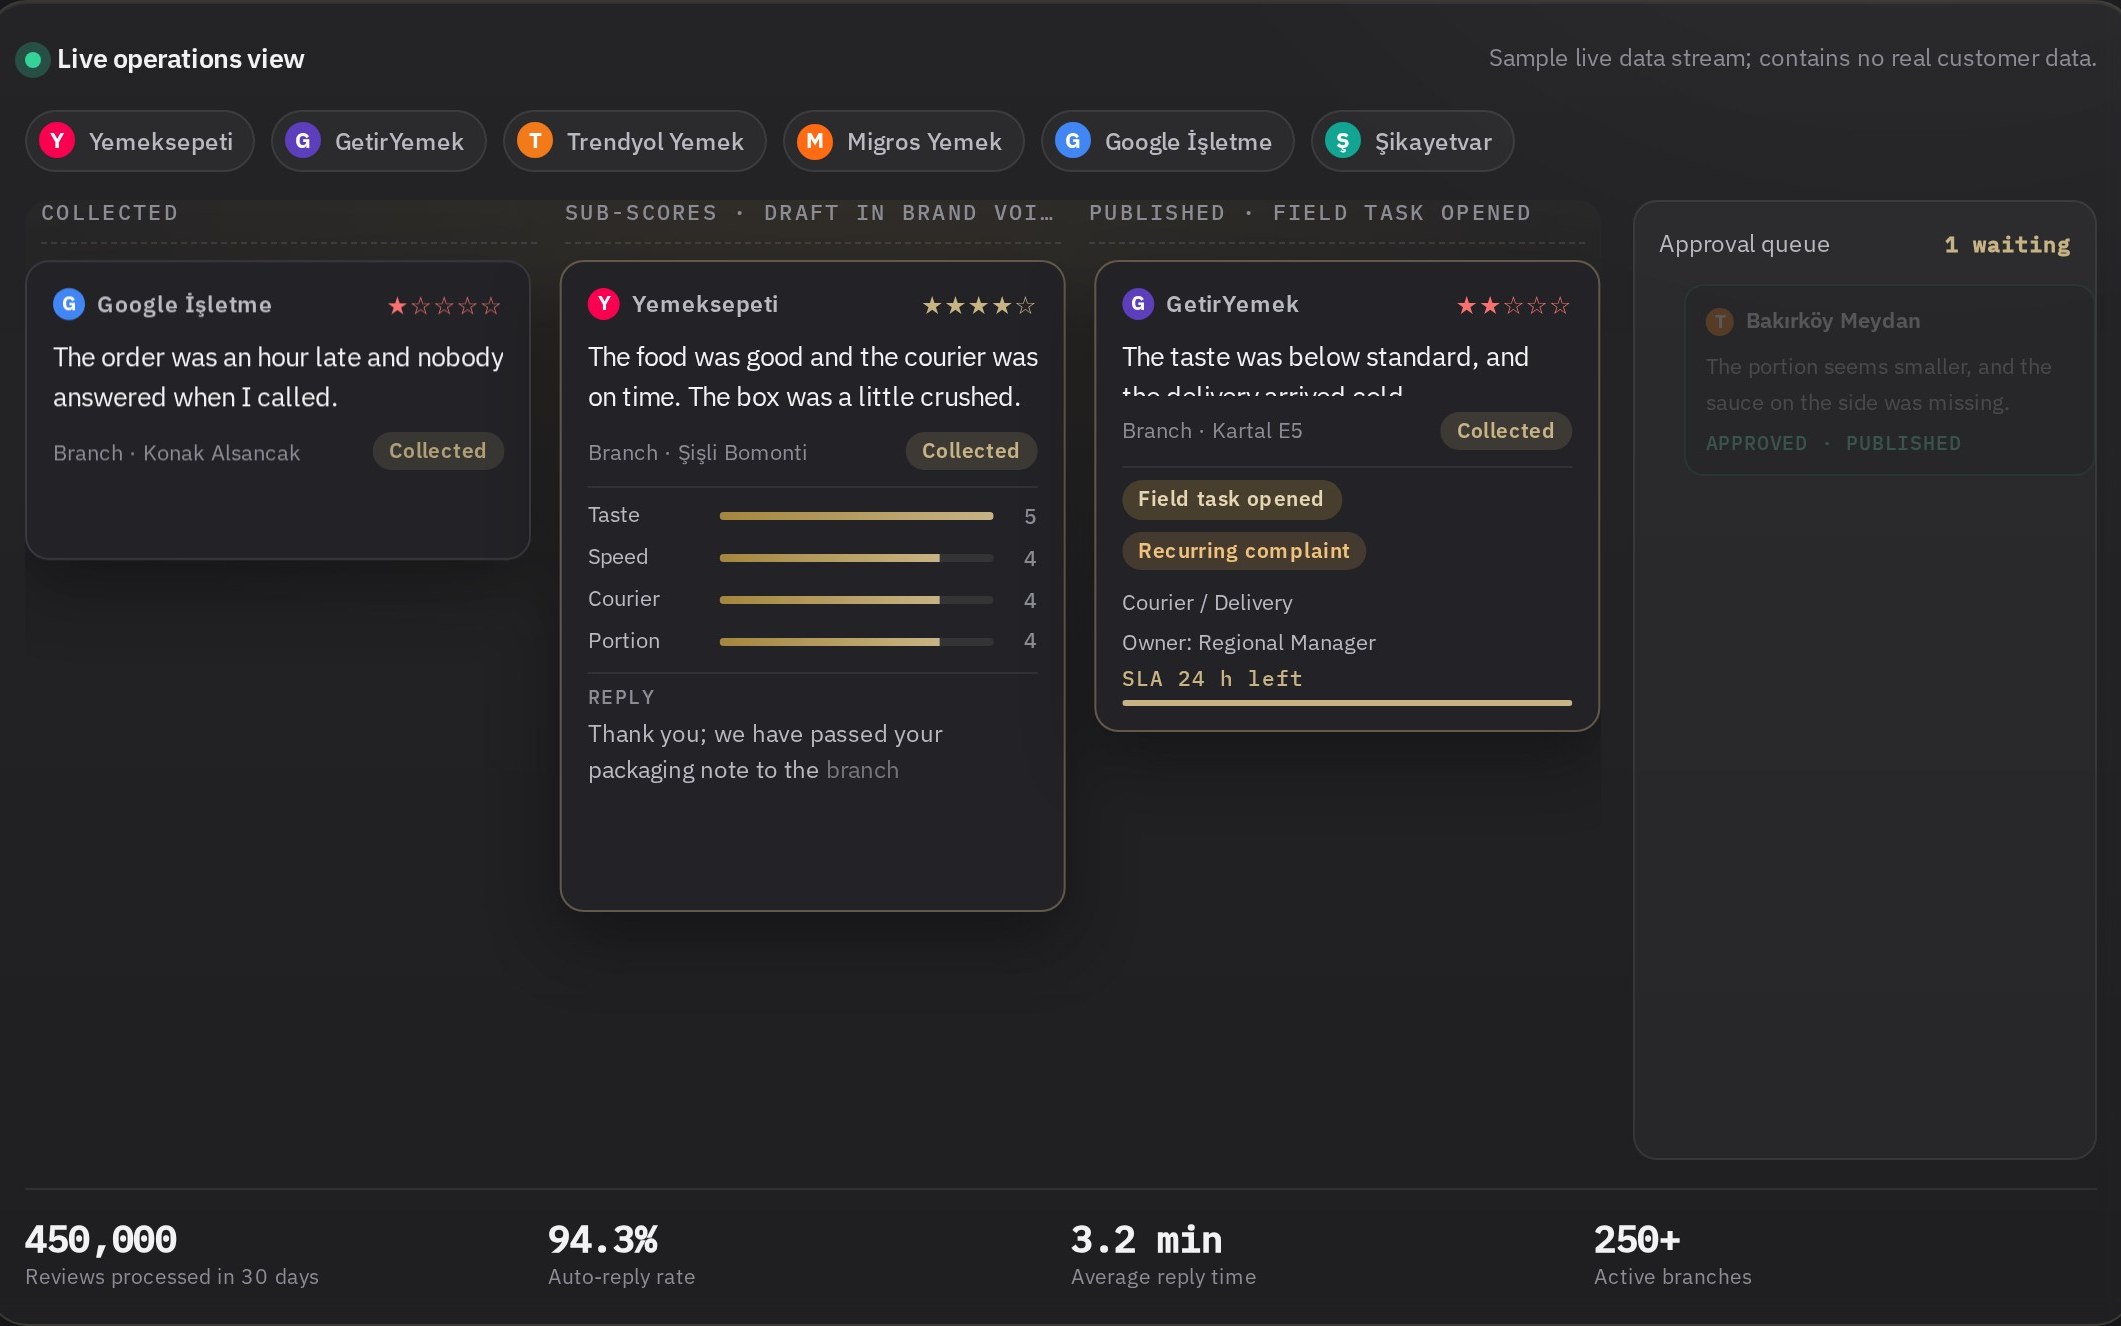
The system speaks in your brand's name; that is why what it did, who approved it and when it was published must always be visible. Roles are separated by permission boundaries and personal data is masked before a reply is generated.
LiveRecords, roles, masking.
What it does
Assurance rests on four pillars; none of them is optional.
- Service continuity
- Scan cycles are monitored; interruptions are recovered automatically.
- Every step on record
- Who published what, who approved it, when it was published: all recorded.
- Role-based access
- Approver, auditor and operations roles are separated with clear permission boundaries.
- Data-protection-compliant processing
- Personal data is masked automatically before a reply is generated.
Principles
A risky reply never goes out unapproved.
Negative and risky content goes to an authorised approver; the approval record is kept with the reply.
The rules stay with the business unit.
When the brand voice changes, you update the text; you do not depend on a developer or on us.
Demo data is illustrative, the audit is real.
Data on the site and in the demo is illustrative; in a live setup every record carries a real approval and timestamp.
Start with one pilot brand.
Let us define the roles and approval rules for the pilot brand together with your compliance team.